Ufer & Company Insurance
Ann Arbor, MI:
Lawfulness of Financial Crime Data Processing Under GDPR
Much that has been written about the General Data Protection Regulation (GDPR) relates to the burden of obtaining proper consents in order to process data. This general theme has provoked questions about whether and how financial institutions can process data to fight financial crime if they need consent of the data subject. While there are certainly valid questions, GDPR is much more permissive to the extent data is used to prevent or monitor for financial crime. Clients and counterparties will often be more…
How you can package, market and sell GDPR-compliant Data Protection products
The European Union (EU) General Data Protection Regulation (GDPR) that is coming into effect on May 25, 2018, presents a great opportunity for Acronis value-added resellers (VARs) to offer GDPR-compliant products to companies and organizations affected by the new regulation. GDPR is designed to regulate the processing of personal data of European Union residents irrespective of whether the company handling that data is based in Europe…
CIO upfront: What should you be doing to manage your GDPR risks?
The British regulator has fired the first shot across the bow of foreign companies processing European personal data, writes Frith Tweedie of EY
FIS to Buy Worldpay in Record $34 Billion Payment Processing Deal
The deal is a part of a wider consolidation within the $1.4 trillion financial processing world, which is ripe for mergers and acquisitions.
Show Me The (Data About The) Money! What You Didn’t Know About Data Aggregation Can Hurt You.
Everyone wants access to consumer financial data. This might be why Visa is paying $5.3 billion for Plaid, one of the biggest U.S. data aggregators – entities that access, aggregate, store, and share consumer financial data they get from banks. It is time we created better data protection standards.
Financial Compliance Shouldn’t Be an Extreme Sport
What do financial compliance and skydiving for the first time have in common? Well, both can cause the same symptoms: sweaty palms, trembling limbs, and an unsettled feeling around the stomach area. Yet, when done right, both can make you feel proud,...

Can Big Data Be Humanized?
Is big data, with its innumerable data points and previously undreamt-of processing power, all it’s supposed to be? Or are we missing the forest for the trees?These are the issues presented in a new book by Colin Strong, a market researcher, speaker, and writer. His book,

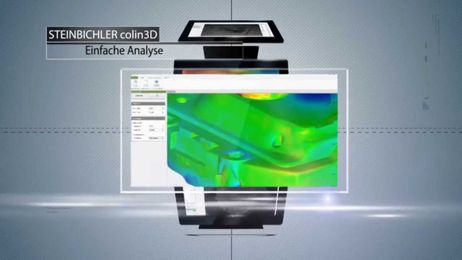
Data acquisition, Data Processing and Simple Data Comparison software
The STEINBICHLER colin3D software for data acquisition, data processing and simple data comparison is a high performance companion for the COMET, Photogramme...
What Can Real-Time Data Analytics Do for Higher Education?
Processing continuous streams of data allows universities to improve student academic performance, safety initiatives and building maintenance on campus.

How to Automate Invoice Data Entry in MYOB Advanced ERP System
Video screencast demonstrates automated data entry in MYOB Advanced ERP System with ABBYY FlexiCapture Cloud Invoice Service
How Data Analytics Will Revolutionise Wealth Management
Today we are seeing significant changes in the way financial services information is being curated and delivered. Data analytics and the increasingly widespread use of data visualisation techniques are finding their way into the wealth management industry as firms look for more efficient ways to acquire insight from ever increasing amounts of data to monitor the effectiveness of their products, strategies, and resources. Data visualisation is…
A Deep Dive into Cloud Data Warehousing
Cloud data warehousing has rapidly become the norm. Here’s how to evaluate and implement a cloud data warehousing solution for your enterprise.

Smart Data Solutions Is Set To Install Solar Panels To Their Minnesota Headquarters
/PRNewswire/ -- Smart Data Solutions, a MN based collateral-processing and workflow automation service, will be installing roughly 400 solar panels to the roof...